In the rapidly expanding ecosystem of Web3, the promise of decentralized finance and digital ownership has attracted millions of participants. However, this transition toward a permissionless financial landscape has also drawn the attention of malicious actors who exploit vulnerabilities in user security practices. As the frequency of phishing attacks and wallet-draining schemes rises, understanding the mechanisms of these threats and implementing robust defense strategies has become an existential necessity for every blockchain participant. Security is no longer an optional component of the Web3 experience; it is the foundational layer upon which all digital sovereignty rests.
The Nature of Modern Web3 Threats
The primary vulnerability in the current Web3 landscape is not necessarily the underlying blockchain technology, which remains robust, but rather the human interface—the point where users interact with decentralized applications (dApps). Malicious actors have moved beyond simple social engineering, evolving toward complex, automated systems designed to compromise private keys or obtain unauthorized approval for token transfers.
One of the most pervasive threats involves "token approvals," a mechanism that allows a smart contract to move funds on behalf of a user. While this is a standard feature of decentralized exchanges (DEXs) like Uniswap, scammers create malicious dApps that request infinite or excessive approvals. Once a user grants these permissions, their assets are effectively unlocked, allowing the attacker to drain the wallet at their convenience.
Chronology of a Typical Compromise
The lifecycle of a typical wallet drain attack generally follows a consistent pattern, regardless of the specific platform or token involved.
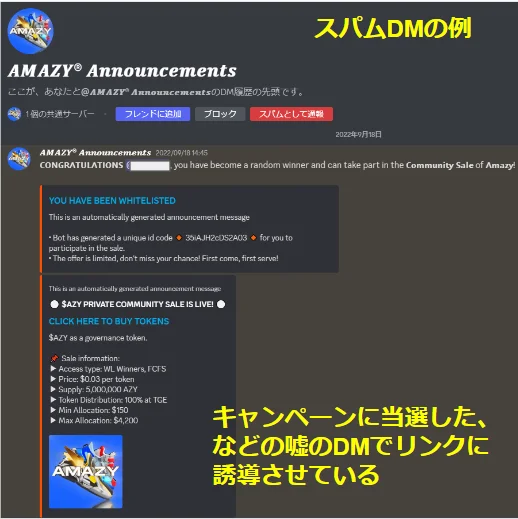
- The Lure: Attackers often use social media platforms, particularly X (formerly Twitter) and Discord, to distribute malicious links. These links often masquerade as official project announcements, airdrop notifications, or urgent security alerts requiring "immediate verification."
- The Connection: Upon clicking a malicious link, the user is prompted to connect their wallet (e.g., MetaMask or Trust Wallet). This is the initial point of vulnerability.
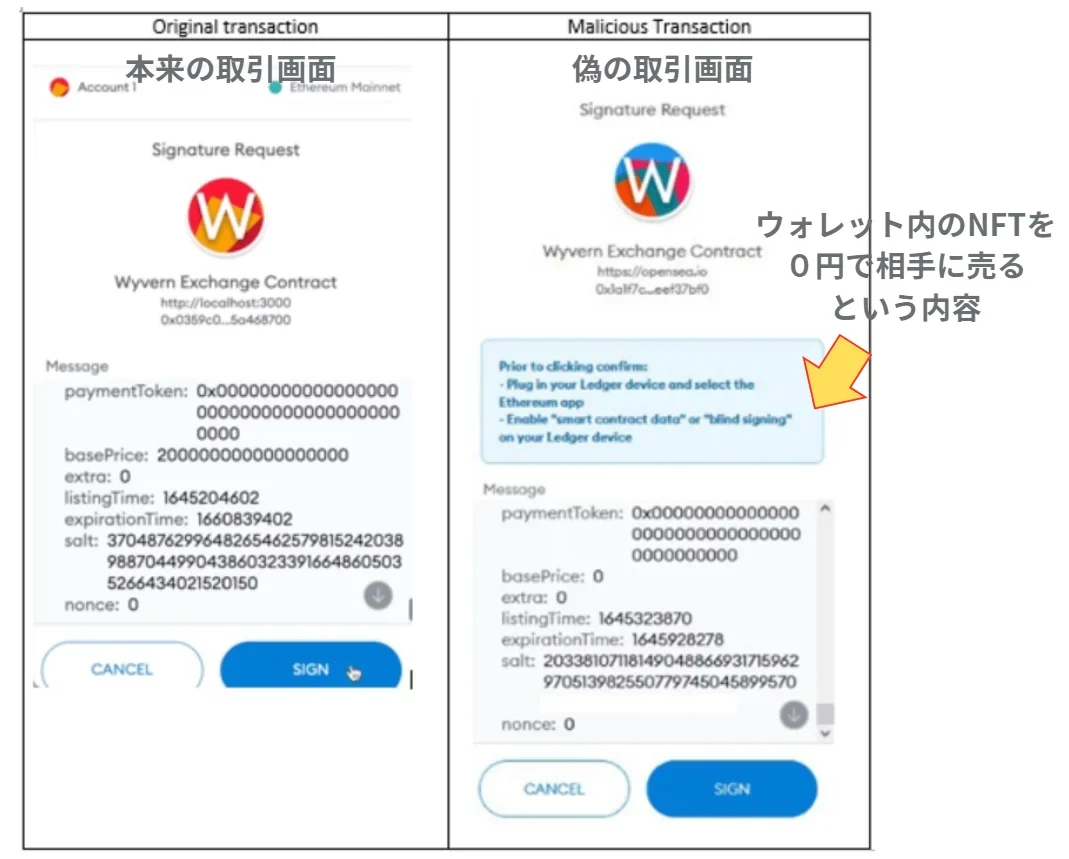
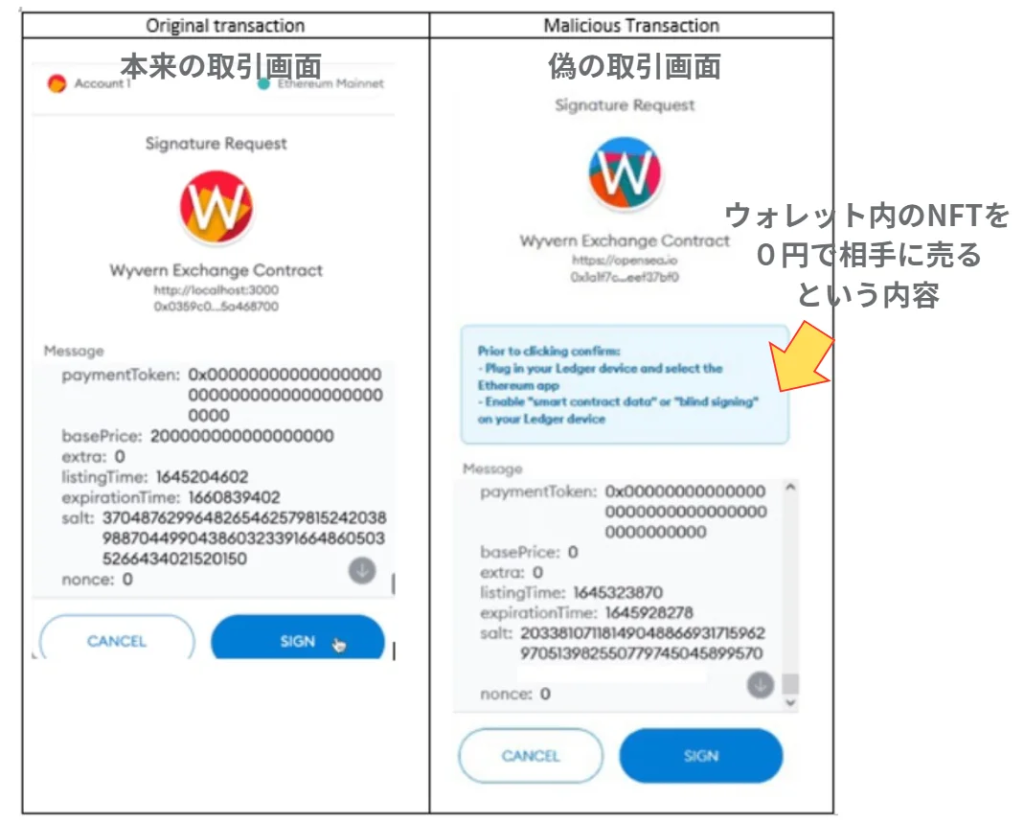
- The Malicious Approval: The dApp interface requests a signature or a transaction approval. Often, these requests are obfuscated or hidden behind legitimate-looking buttons. Users, believing they are interacting with a reputable service, grant the request.
- The Exploitation: Once the approval is granted, the smart contract interacts directly with the user’s assets. Because the smart contract has been granted the authority to transfer tokens, the attacker can move the funds to their own address without needing the user’s private key.
- The Aftermath: The transaction is recorded on the blockchain (such as Etherscan for Ethereum or BscScan for BNB Chain). Once the funds have moved, they are typically funneled through "mixers" or decentralized privacy tools to obfuscate their origin, making recovery nearly impossible.
Data and Statistical Context
According to reports from leading blockchain security firms, the cumulative loss from Web3-related scams and phishing attacks reached multi-billion dollar levels in the last fiscal year. A significant portion of these losses is attributed to "permit" signature exploits and blind signing—where users sign messages without fully comprehending the underlying data. Data indicates that over 70% of wallet drain incidents could have been prevented if users had verified the transaction’s destination and permissions before signing.
The Role of "Revoking" Approvals
For users who have inadvertently connected to suspicious dApps or granted excessive permissions, the "Revoke" function is the most effective defensive tool. Revoking allows a user to terminate the ability of a smart contract to access their tokens.
To perform a revocation:
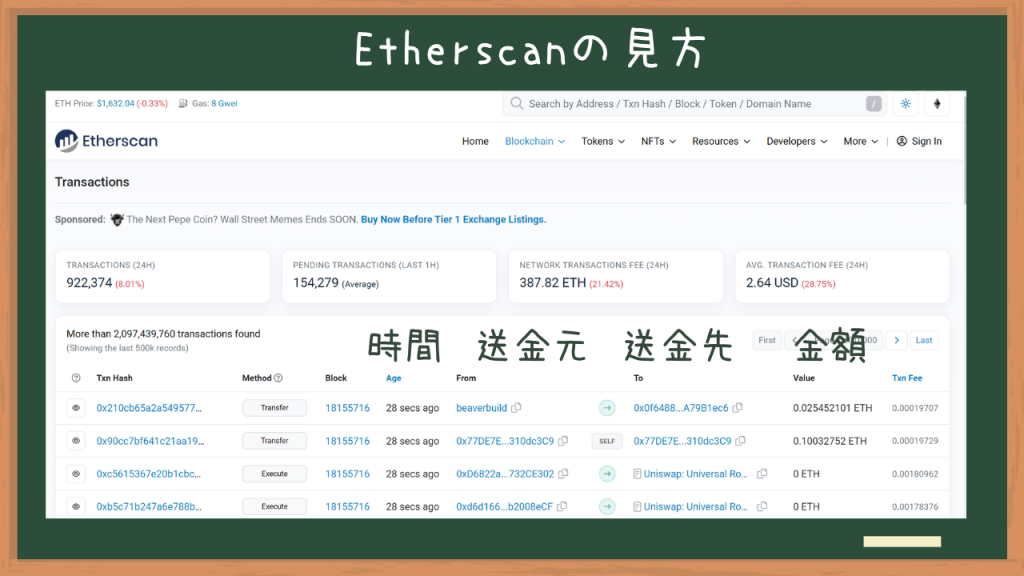
- Access a reputable blockchain explorer like Etherscan (for Ethereum) or BscScan (for BNB Chain).
- Navigate to the "More" or "Token Approval" section.
- Connect your wallet to the explorer.
- Review the list of active approvals. Any unfamiliar or suspicious contracts should be revoked immediately.
This process essentially resets the security posture of the wallet, ensuring that previous interactions no longer pose an active threat to current holdings.
Expert Analysis and Best Practices
Security experts emphasize that the decentralized nature of blockchain means that the responsibility for asset protection lies entirely with the individual. Unlike traditional banking, there is no centralized authority to reverse unauthorized transactions. Therefore, the "zero-trust" model is the most effective approach to Web3 navigation.
Key recommendations for minimizing risk include:
- The Principle of Minimum Access: Never grant more permissions than necessary. If a dApp asks for approval for an entire asset balance when only a small fraction is being traded, reject the transaction.
- Secondary Wallets: Segregate your assets. Use one "cold" wallet for long-term storage of high-value assets and a "burner" wallet with limited funds for interacting with new or experimental dApps.
- Verification of Channels: Official announcements will rarely be sent via Direct Message (DM). If you receive a DM regarding an urgent security update or an exclusive offer, assume it is a scam. Always verify information through the project’s official, verified social media handles.
- Use of Security Tools: Utilize browser extensions like Kekkai or other security-focused dApps that monitor transactions and warn users before they sign a potentially malicious contract. These tools act as a final layer of defense by parsing the transaction data into human-readable warnings.
Implications for the Future of Web3
The prevalence of these scams poses a significant barrier to mainstream adoption. As the industry matures, there is an increasing demand for better user interface (UI) and user experience (UX) designs that make transaction data more transparent. Projects that prioritize "security-by-design"—where transaction signatures are clearly explained in plain language—are likely to gain greater trust among users.
Furthermore, the industry is seeing a shift toward "Account Abstraction," a development that could allow for more programmable security features at the wallet level. This would enable users to set spending limits, require multi-signature authentication for large transactions, and even pause their wallets in the event of a suspected compromise.
Conclusion
The evolution of Web3 security is a constant arms race between innovation and exploitation. While the technology offers unprecedented freedom and financial autonomy, it requires a high degree of digital literacy. By maintaining a disciplined approach to wallet management, consistently revoking unnecessary permissions, and remaining skeptical of unsolicited communications, users can significantly mitigate their exposure to the threats that currently plague the ecosystem. In the world of blockchain, vigilance is the ultimate safeguard. As we move forward, the collective responsibility of developers and users to advocate for clearer, more secure standards will define the sustainability of the decentralized movement.