The rapid expansion of the Web3 ecosystem, while driving unprecedented innovation in decentralized finance (DeFi), non-fungible tokens (NFTs), and blockchain gaming, has simultaneously created a fertile landscape for cybercriminals. As users increasingly interact with decentralized applications (dApps) and smart contracts, the risk of asset theft through malicious signatures and unauthorized token approvals has reached an all-time high. Protecting digital assets in this environment requires a fundamental understanding of how blockchain interactions function and the specific security protocols necessary to safeguard a crypto wallet.
The Anatomy of a Web3 Security Breach
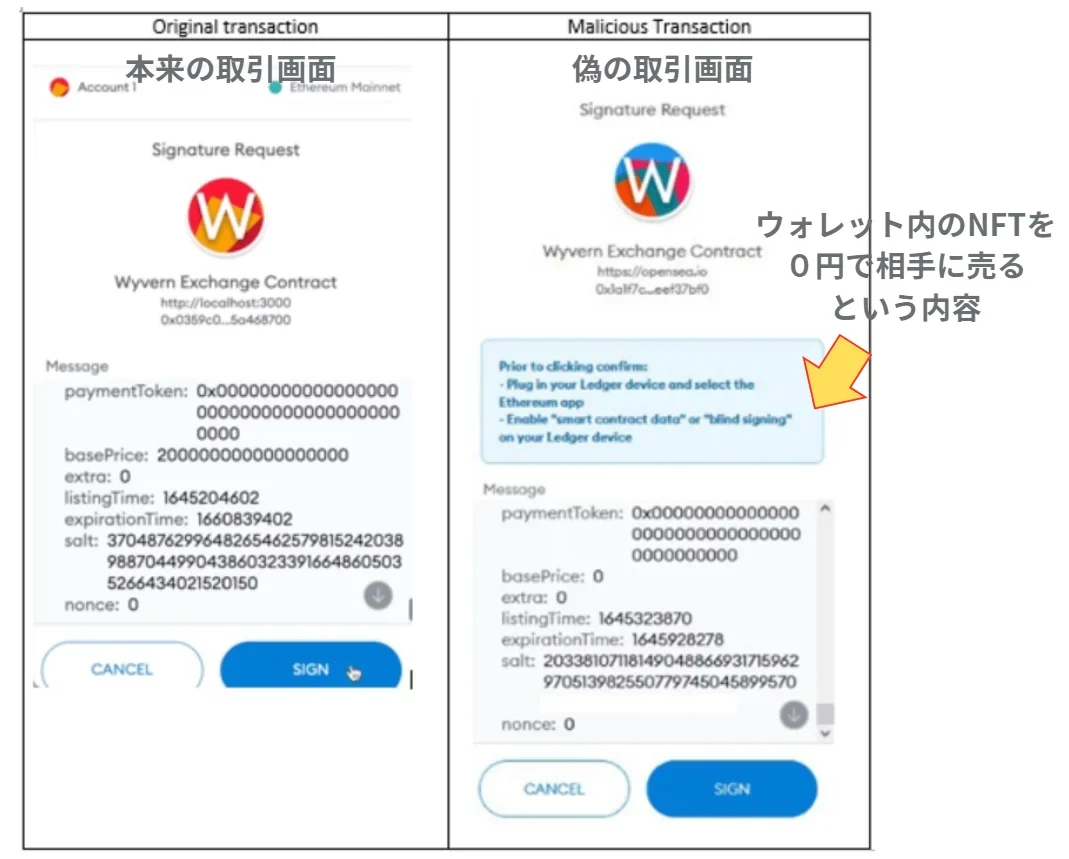
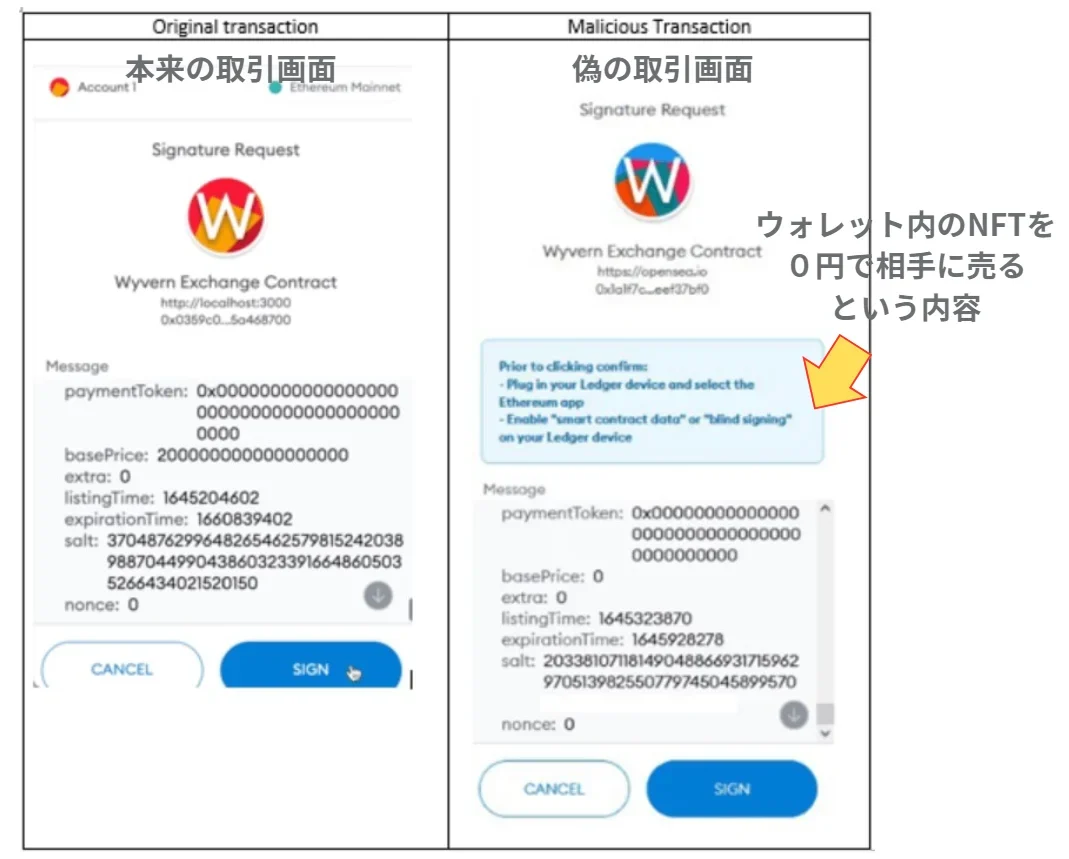
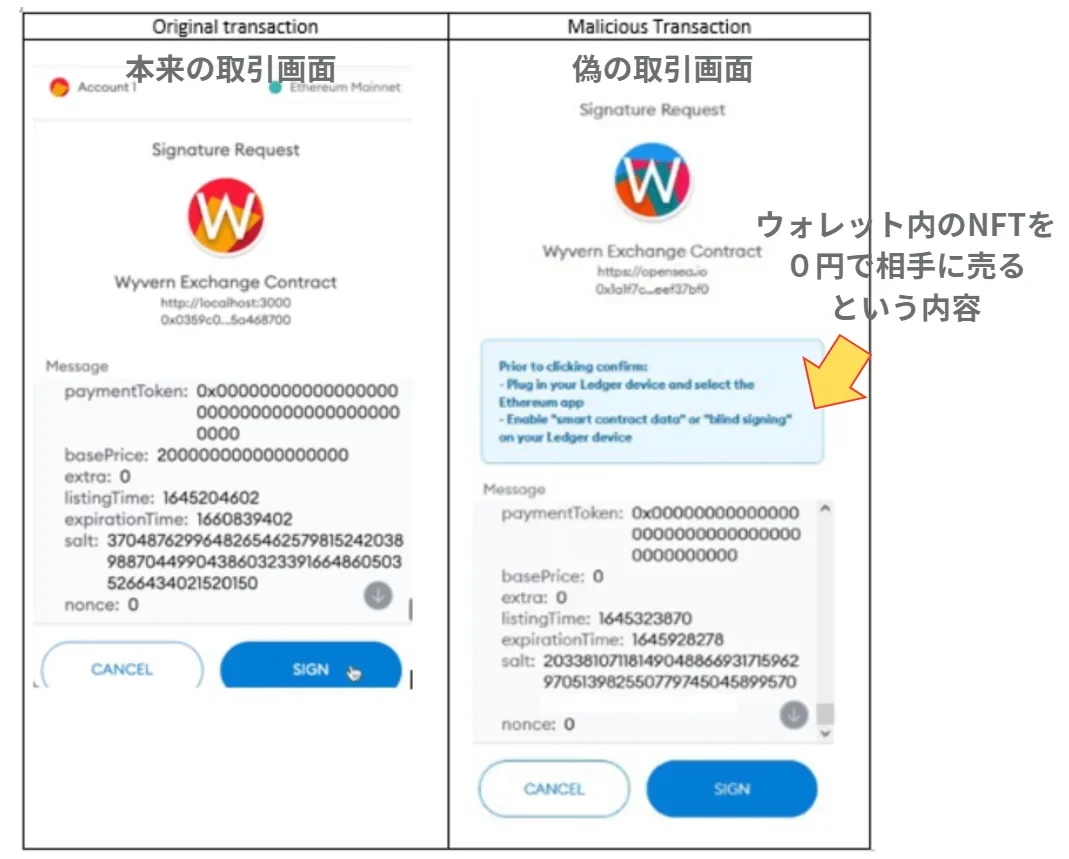
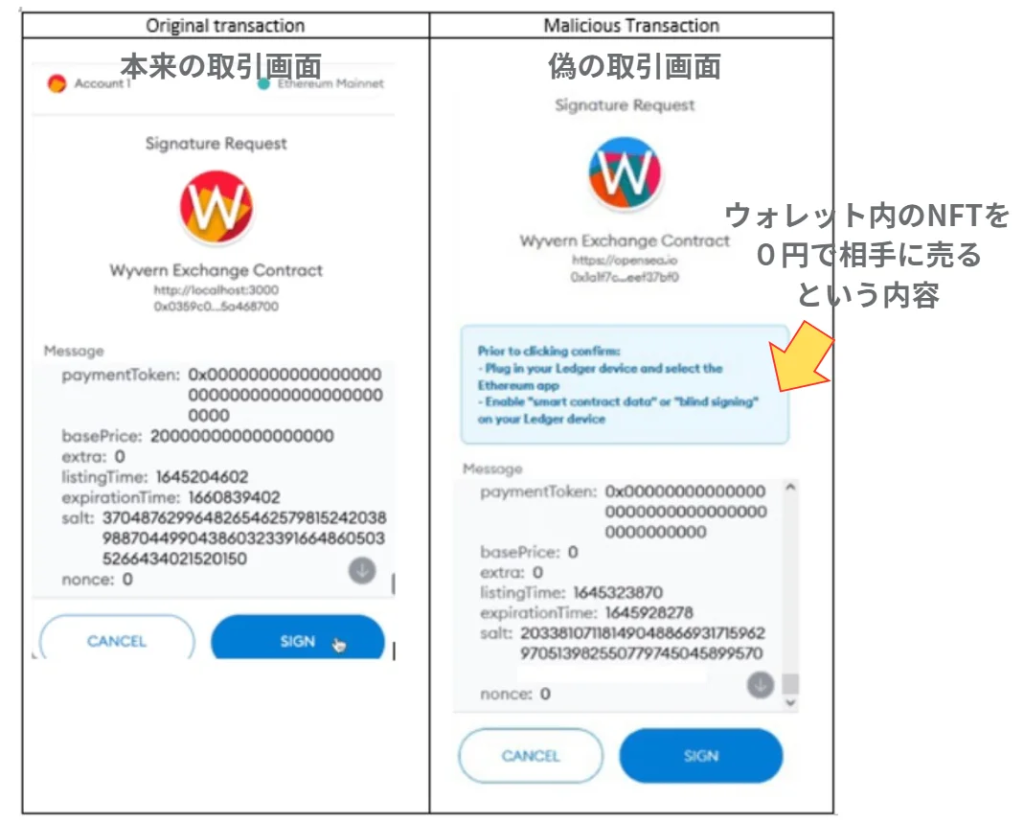
At the core of many modern Web3 attacks is the exploitation of "token approvals." When a user interacts with a dApp, they are often required to sign a transaction that grants the smart contract permission to access or spend tokens from their wallet. This mechanism is essential for decentralized exchanges and NFT marketplaces to function. However, malicious actors frequently design fraudulent dApps or compromise legitimate sites to inject malicious code that requests "unlimited" or excessive spending allowances.
Once a user signs such a transaction, the malicious contract gains the technical authority to drain the user’s wallet of those specific assets at any time. Because these transactions are executed on-chain, they are often irreversible, making prevention the only viable defense. Security experts warn that users often overlook the technical details of the permissions they are granting, treating them as simple "connect wallet" prompts rather than legal and financial authorizations.
Chronology of Evolving Threat Vectors
The evolution of Web3 security threats can be traced through several distinct phases. In the early stages of the DeFi boom, attacks primarily focused on smart contract vulnerabilities—coding errors that allowed hackers to drain liquidity pools. As protocols matured and security audits became standard, attackers shifted their focus toward the "human element."
- The Phishing Era: Early 2022 saw a surge in phishing campaigns, where attackers cloned popular NFT project websites to harvest private keys or seed phrases.
- The Approval Exploit Era: Throughout 2023, the industry observed a transition toward "set approval for all" exploits. Attackers realized that tricking a user into signing a malicious permit transaction was more efficient than attempting to steal a private key.
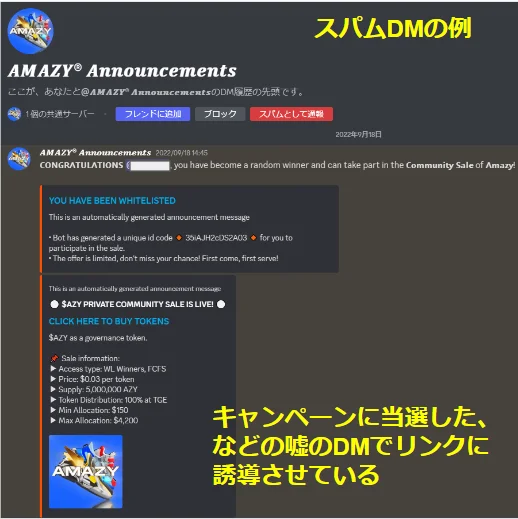
- The Current Landscape: Today, malicious direct messages (DMs) on platforms like Discord and X (formerly Twitter) serve as the primary delivery mechanism for these exploits. Attackers often pose as support staff or project founders, luring users to "verify" their wallets on a malicious site, which then executes the drainer code.
Statistical Context and Market Impact
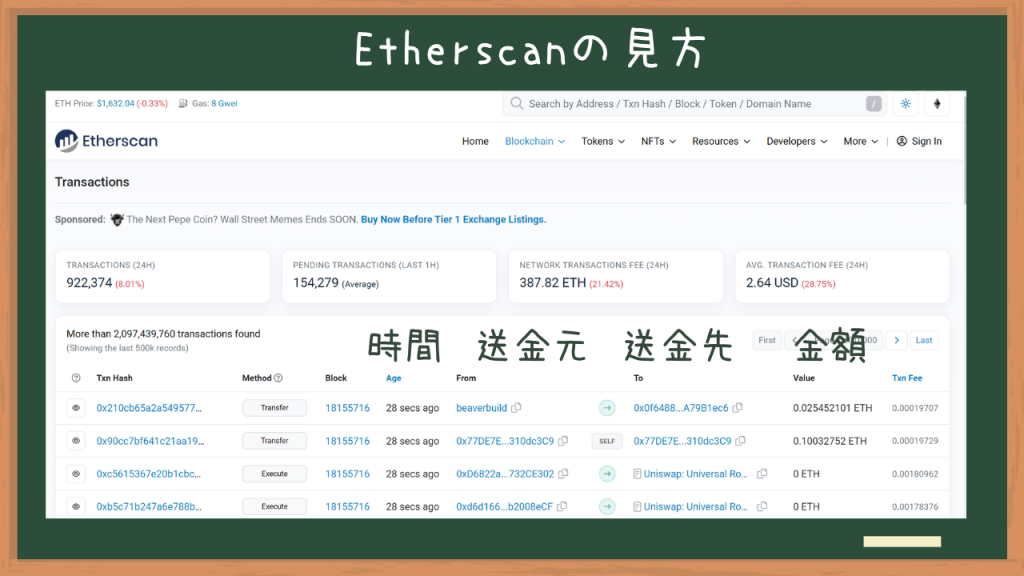
Data from blockchain security firms indicates that billions of dollars are lost annually to these types of exploits. Etherscan and BscScan, the primary block explorers for the Ethereum and Binance Smart Chain networks, have become critical tools for users to monitor their wallet’s health.
According to industry reporting, a significant percentage of wallet drainage incidents are attributed to users interacting with unverified or "blind" contract signatures. While total volume of lost assets fluctuates with market conditions, the frequency of these attacks remains consistent. Security analysts suggest that if users were to regularly audit their token approvals, the success rate of these malicious drainers would drop by an estimated 60 to 70 percent.
The "Revoke" Protocol: A Necessary Security Habit
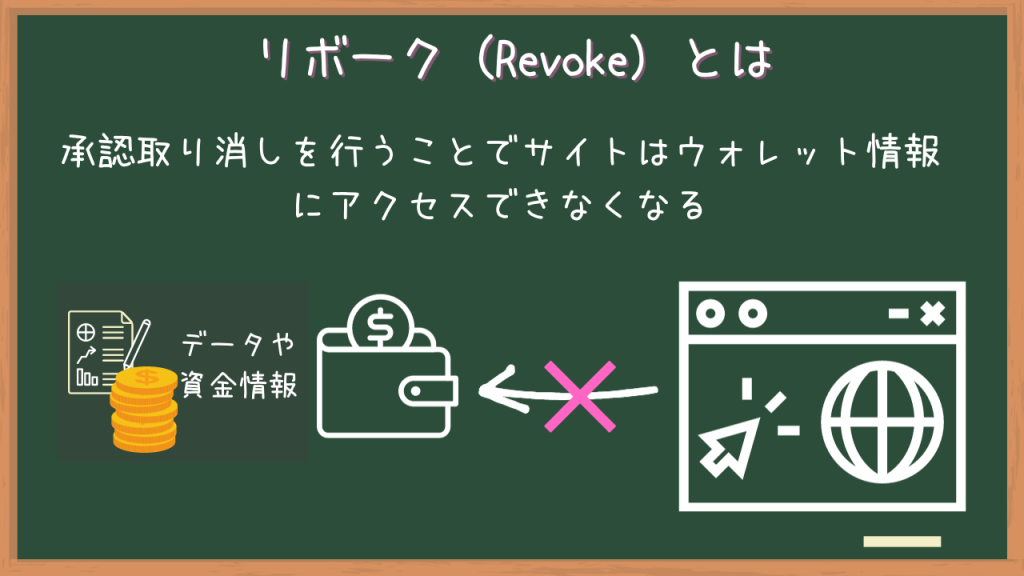
To combat the risk of unauthorized access, the concept of "Revoking" has become a cornerstone of Web3 security hygiene. Revoking is the process of updating the smart contract state on the blockchain to terminate a previously granted spending allowance.
Security professionals emphasize that users should view token approvals as temporary permissions rather than permanent states. If a user interacts with a new or less-known dApp, it is considered a best practice to revoke access to that dApp immediately after the transaction is complete. Many reputable security tools, such as Revoke.cash, allow users to view every contract currently authorized to spend their tokens and provide a user-friendly interface to cancel those permissions.
Step-by-Step Guide to Auditing Wallet Permissions
For users looking to secure their digital assets, the process of auditing and revoking permissions is straightforward and requires no advanced technical knowledge:
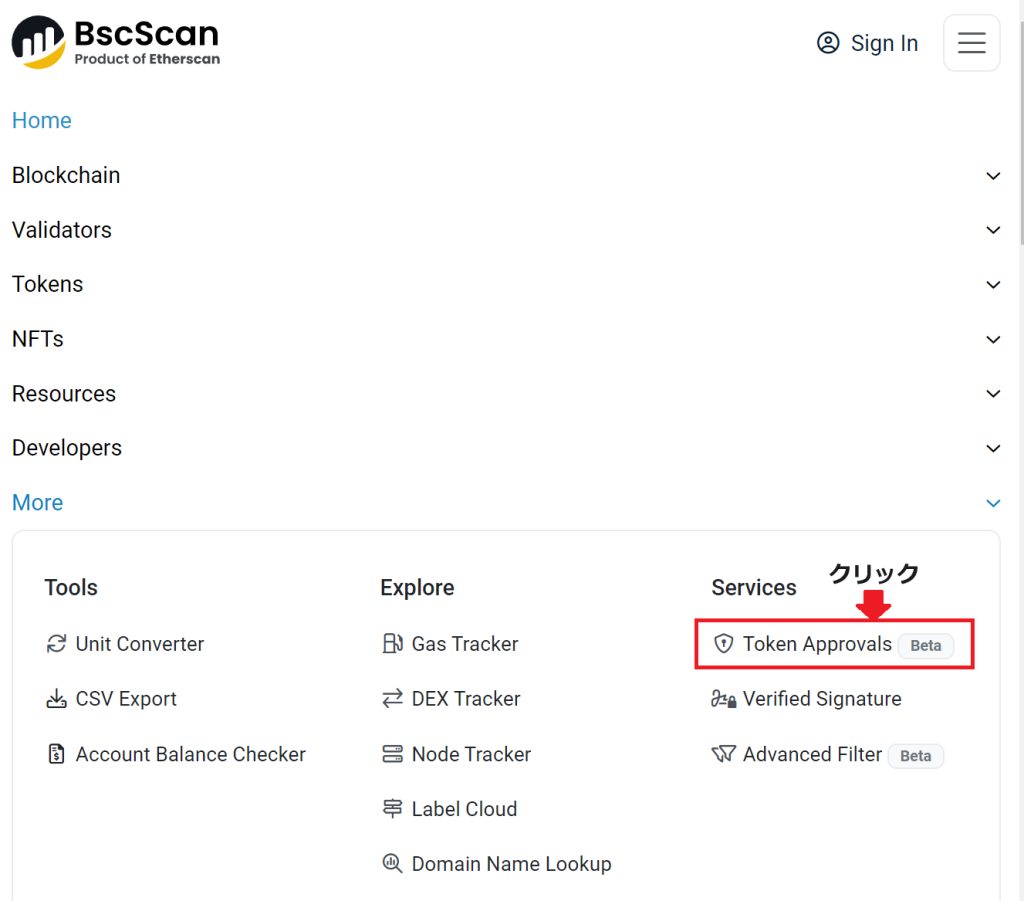
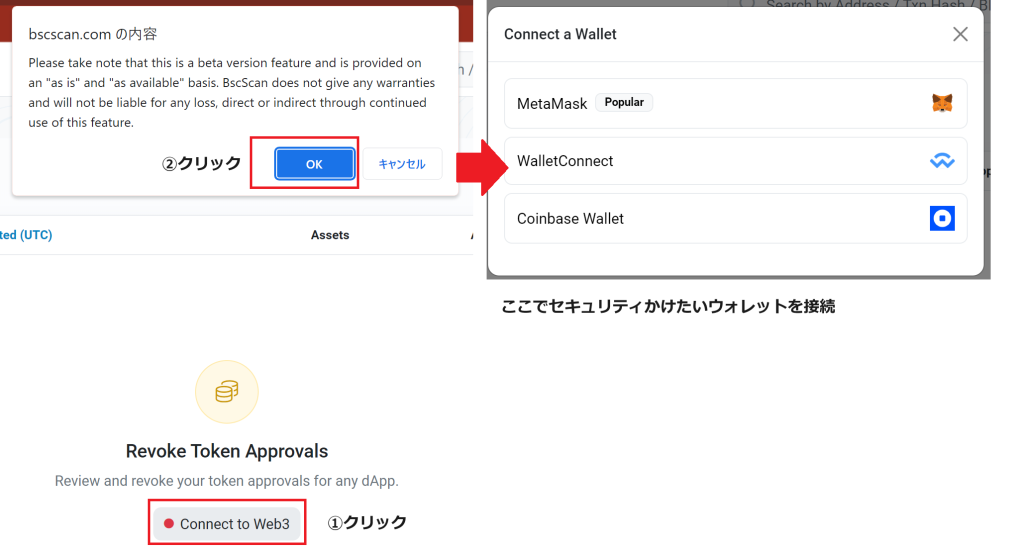
- Access a Trusted Revocation Tool: Navigate to a reputable service such as Etherscan’s "Token Approval" portal or a dedicated revocation site. Ensure the URL is correct to avoid falling for a phishing site.
- Connect Your Wallet: Use a secure interface to connect the wallet you wish to audit. Avoid connecting your primary "cold" storage wallet to unknown or high-risk sites.
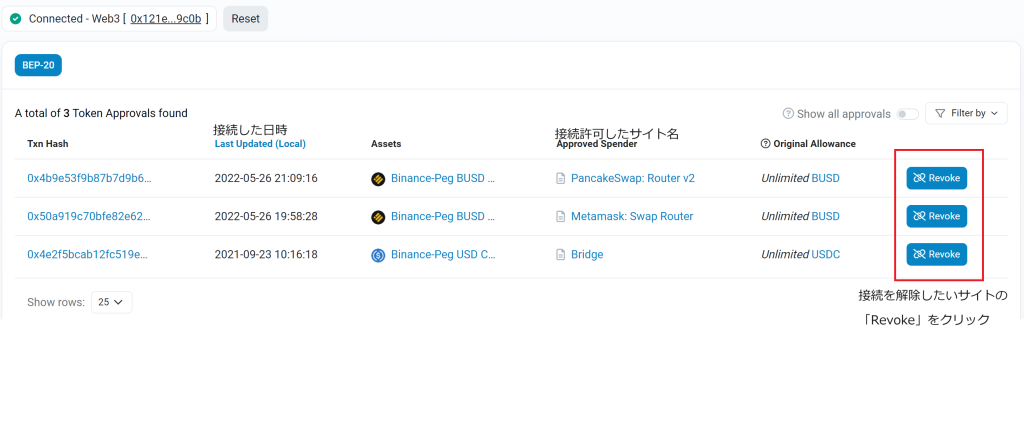
- Review Active Approvals: Once connected, the interface will display a list of all tokens and the contracts currently authorized to spend them. Pay close attention to contracts that have "Unlimited" spending limits.
- Execute the Revoke Function: Select the specific contract you wish to remove and click the "Revoke" button. This will trigger a transaction in your wallet that you must sign.
- Confirm on-chain: Once the transaction is processed on the blockchain, the permission is officially terminated.
The Role of Decentralized Identity and Caution
Beyond technical tools, the most effective defense remains skepticism. Most professional Web3 projects will never initiate contact via DMs on social media to ask for wallet verification. Official support staff will rarely, if ever, request that a user connect their wallet to a "verification" site to fix an issue.
Experts advise users to adopt a "zero trust" mindset. Before signing any transaction, one should verify the site’s domain, cross-reference social media accounts, and utilize browser-based security extensions like Kekkai, which provide real-time alerts when a signature request appears suspicious. These extensions analyze the nature of the transaction and can warn the user if a contract is known to be associated with malicious activity.
Implications for the Future of Web3
As the industry moves toward mass adoption, the responsibility for security is shifting from the individual to the infrastructure. We are seeing a rise in "Account Abstraction," a technology that allows for more flexible wallet features, such as pre-set spending limits and multi-signature requirements, which could eventually render the current "set approval" exploit obsolete.
However, until such technologies are universally integrated, the burden of vigilance remains on the user. The distinction between a secure wallet and a compromised one often comes down to the user’s willingness to perform routine maintenance. By treating blockchain addresses as high-value digital bank accounts rather than anonymous gaming wallets, users can significantly mitigate their exposure to the persistent threats of the Web3 landscape.
Conclusion: A Proactive Stance
The landscape of Web3 is inherently adversarial. Every transaction is a potential point of failure if not handled with care. The tools to secure one’s assets—block explorers, revocation portals, and security-focused browser extensions—are widely available and free to use. By normalizing the habit of auditing token approvals and maintaining a healthy suspicion of unsolicited requests, users can participate in the growth of decentralized finance while ensuring their digital legacy remains protected from those who seek to exploit the vulnerabilities of the new digital economy. Security is not a one-time setup; it is an ongoing practice of due diligence, constant monitoring, and the disciplined use of defensive protocols.