Cryptocurrency exchange Bitget has released a comprehensive update regarding the high-profile security breach that shook the digital asset community earlier this week. In its latest transparency report, the platform revised its confirmed losses upward to approximately $387.5 million, a notable increase from the initial estimate of $351.6 million. According to exchange representatives, the upward revision stems from meticulous ongoing transaction tracing rather than any secondary wave of unauthorized outflows. As the platform works to secure its infrastructure, it has also unveiled a carefully structured, multi-day schedule to restore normal withdrawal services for its global user base, marking a critical turning point in the aftermath of the incident.
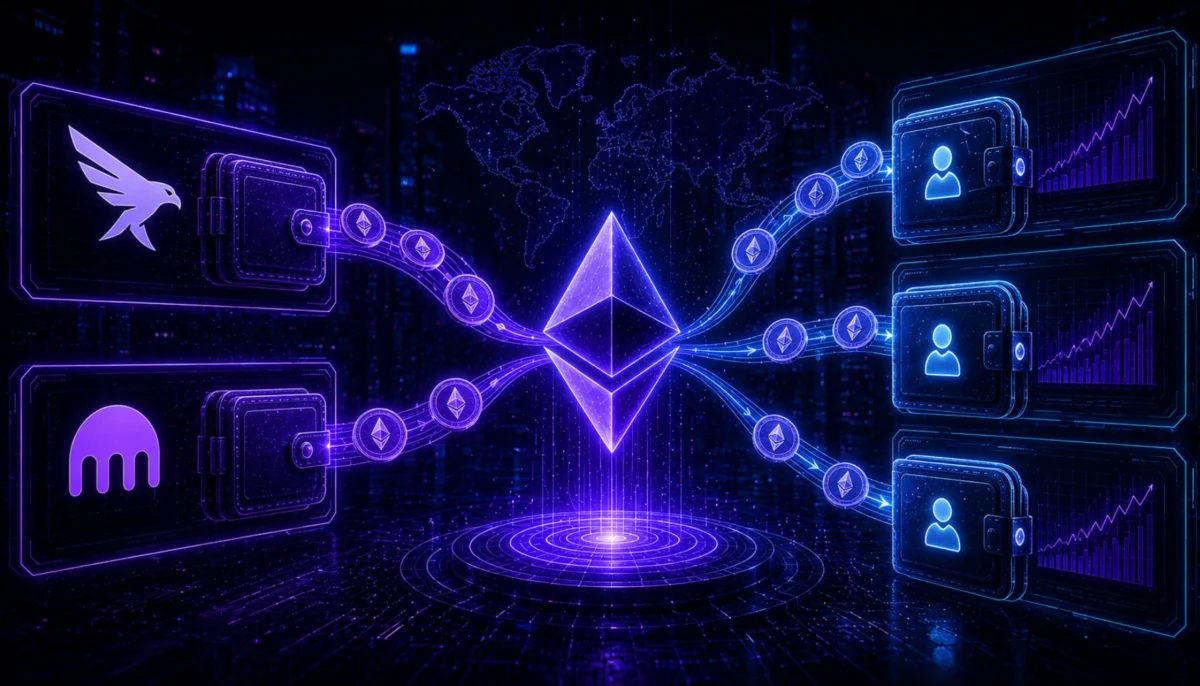
The scale of the breach places it among the most significant security events faced by a centralized cryptocurrency platform in recent months. The affected funds span multiple blockchain networks and token standards, encompassing Ethereum and various Ethereum Virtual Machine (EVM) compatible chains, the XRP Ledger, Zcash, and the TRON network. This cross-chain proliferation of the exploit highlights the sophisticated nature of the attack, which bypassed existing internal controls before security teams managed to isolate and contain the vector.
Anatomy of the Exploit and Remediation Efforts
In the immediate wake of the breach, Bitget’s engineering and security personnel initiated a rigorous internal audit, working in tandem with prominent third-party blockchain security and forensic firms, including Mandiant and SlowMist. According to official disclosures, the investigation has successfully pinpointed the exact attack path and the methodology utilized by the malicious actors to circumvent established security protocols.
Bitget has confirmed that the underlying vulnerability has been fully patched, closing the door on any possibility of further unauthorized asset transfers. However, tracing funds across diverse cryptographic ledgers remains a complex logistical challenge. The revised loss figure of $387.5 million reflects the culmination of exhaustive ledger analysis, as forensic specialists mapped out secondary wallet addresses and identified additional capital movements that were not immediately visible during the chaotic first hours of the incident.
To accelerate recovery efforts, Bitget has introduced a targeted recovery bounty program. The initiative is designed to incentivize external security researchers, white-hat hackers, and blockchain analysts. Under the terms of the program, eligible parties whose voluntary, authorized actions directly result in the freezing or recovery of stolen funds will receive a bounty calculated as a percentage of the secured assets. The exchange noted that this collaborative approach has already yielded tangible results, with a portion of the stolen funds successfully frozen through active coordination with industry partners, centralized exchanges, and liquidity providers.
The Phased Withdrawal Schedule and Operational Stress Test
With the technical vulnerabilities contained, the immediate operational focus for Bitget has shifted toward the restoration of platform liquidity and user access. Rather than lifting restrictions simultaneously—a move security experts generally discourage due to potential system bottlenecks and residual risks—Bitget has opted for a methodical, phased rollout of its withdrawal services.
The staggered timetable serves as an essential operational stress test for the platform. The phased reopening is scheduled to proceed according to the following timeline:
- September 28: Bitcoin (BTC) withdrawals are scheduled to reopen first, allowing users to reclaim access to the flagship digital asset.
- September 29: Ether (ETH) and associated token withdrawals across several supported layer-1 and layer-2 networks will resume.
- September 30: Tether (USDT) withdrawals will be activated, restoring access to the market’s primary stablecoin liquidity layer.
- October 2: All remaining tokens, fiat services, and peer-to-peer (P2P) withdrawal channels are planned to be fully operational.
This schedule represents a high-stakes operational test for the exchange. While Bitget leadership has repeatedly reassured its user base that customer account balances remain fully intact—backed by internal reserves and asset protection guarantees—the true test of market trust will occur when withdrawal gates finally swing open. Industry observers will be watching closely to see whether the platform experiences abnormal liquidity pressure or if the managed rollout successfully prevents panic-driven runs on platform reserves.
Broader Implications for Centralized Crypto Exchanges
The Bitget security incident reverberates far beyond the company’s internal operations, serving as a stark reminder of the persistent systemic risks facing centralized cryptocurrency exchanges (CEXs). Despite the implementation of multi-signature architectures, cold storage solutions, and advanced intrusion detection systems, malicious actors continue to exploit sophisticated zero-day vulnerabilities, complex logic flaws, and cross-chain bridging mechanisms.
The inclusion of multiple disparate networks in this breach—ranging from account-based models like Ethereum to UTXO-based chains like Zcash—demonstrates that modern hackers are increasingly adept at executing multi-chain heists. This trend complicates both defense and recovery, requiring exchanges to maintain deep cross-chain surveillance capabilities and instantaneous communication channels with node operators and rival platforms across the entire blockchain ecosystem.
Furthermore, the incident highlights the growing importance of transparent communication during crises. By continuously updating loss figures, detailing the involvement of reputable forensic auditors like Mandiant and SlowMist, and establishing clear, predictable timelines for the resumption of services, Bitget has attempted to set a standard for crisis management in the digital asset sector. How the market reacts over the coming days as withdrawals resume will likely shape the playbook for how centralized platforms handle catastrophic security breaches moving forward.
For Bitget, stopping the bleeding and patching the code constituted the first crucial phase of crisis resolution. The next phase—safely restoring liquidity, honoring user withdrawals, and successfully recovering stolen capital—will ultimately determine the long-term reputation and viability of the exchange in an increasingly competitive and security-conscious market.