
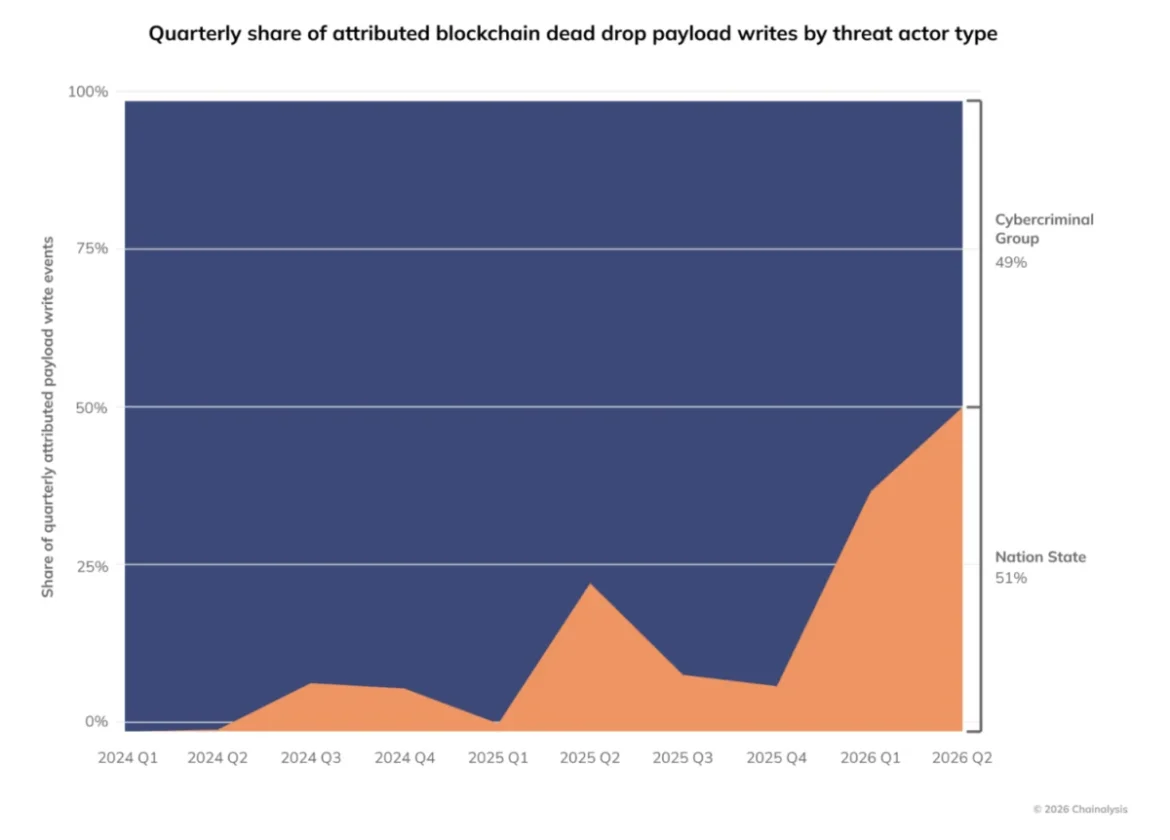
Cybersecurity researchers and blockchain intelligence firms are sounding the alarm over a surging underground tactic that allows malicious actors to maintain permanent, censorship-resistant control over compromised digital networks. Rather than storing their operational code, command-and-control (C2) servers, and malware instructions on centralized web hosting platforms that are vulnerable to law enforcement seizures, domain takedowns, and corporate blocking, modern threat actors are increasingly turning to public blockchains. This methodology—dubbed "blockchain dead drops" (BDDs)—leverages the immutable and decentralized nature of distributed ledgers to create durable, tamper-proof communication channels between infected machines and their operators.

According to recent telemetry and threat intelligence insights from blockchain analytics firm Chainalysis, malicious writes to public blockchains designed to coordinate cyberattacks have spiked exponentially. In the wake of the proliferation of open-source artificial intelligence coding tools, which have drastically lowered the technical barrier to entry for novice and advanced threat actors alike, BDD attacks have surged by 420 percent over a rolling twelve-month period. Daily malicious transactions or smart contract interactions aimed at embedding malware data have skyrocketed from an average of 2.06 writes per day to more than 11.1 writes per day.
This dramatic shift in tactics underscores an evolving paradigm in modern cybersecurity. While traditional threat-intelligence platforms have historically focused on tracking web2 domains, Internet Protocol (IP) addresses, and centralized repositories, the migration of malicious infrastructure to web3 environments has created a distinct visibility gap. State-backed hacking syndicates and financially motivated cybercrime cartels are exploiting this blind spot, transforming public networks into permanent coordination layers that are virtually impossible to take offline through conventional means.

The Evolution and Chronology of Blockchain Dead Drops
While the weaponization of blockchains has accelerated rapidly in recent years, the foundational concepts behind BDDs date back more than a decade. The earliest iteration of on-chain infrastructure hiding emerged in 2013, when operators linked to the Necurs botnet utilized Namecoin—an early fork of Bitcoin—to store C2 domain records. Over the subsequent years, cybercriminals experimented with embedding operational metadata directly into transaction amounts using Satoshis, or writing malicious payloads into the OP_RETURN data field of Bitcoin transactions, a method famously adopted by the Glupteba cryptocurrency mining botnet in 2019.
However, the modern era of BDDs truly materialized in mid-2023 with the advent of "EtherHiding." When infrastructure security providers like Cloudflare clamped down on conventional web servers utilized by the operators of the ClearFake infostealing campaign, the threat actors pivoted. They embedded their malicious delivery scripts directly into smart contracts deployed on the Binance Smart Chain (BSC). Because the underlying blockchain cannot be halted, censored, or administratively seized, the campaign maintained uninterrupted uptime. Within months, unrelated criminal groups—such as the operators behind the Smargaft distributed denial-of-service (DDoS) botnet—began deploying parallel infrastructure.

By late 2024 and early 2025, the tactic graduated from exclusively criminal enterprises to sophisticated, nation-state cyber espionage groups. Intelligence agencies and private sector security researchers identified that state-sponsored actors from Iran and North Korea had integrated BDD frameworks into their advanced persistent threat (APT) playbooks. By Q2 2026, state-linked groups accounted for approximately two-thirds of all newly initiated BDD activity per quarter, fundamentally altering the threat landscape.
Technical Mechanisms: How Blockchain Dead Drops Operate
To understand the resilience of blockchain dead drops, security analysts examine the primary vectors through which threat actors manipulate distributed ledgers. BDD architectures generally bypass the need for traditional hosting by operating in distinct phases: on-chain discovery and off-chain execution. The malware deployed on a victim’s machine is programmed to query public blockchain nodes via remote procedure calls (RPCs) to retrieve specific parameters, routing instructions, or payloads.

Security researchers have identified three primary technical variations of BDD execution:
- Transaction-Based Storage: Threat actors embed encoded C2 configurations, destination IP addresses, or payload pointers directly into transaction metadata fields—such as Bitcoin’s OP_RETURN field or transaction input data on Ethereum Virtual Machine (EVM) compatible chains.
- Contract-Based Storage: Popularized by EtherHiding, this method utilizes smart contracts as dynamic, programmable storage lockers. The attacker updates the internal state of the smart contract whenever their underlying infrastructure changes, and compromised endpoints automatically read the updated contract state to locate active servers.
- Phantom Wallet Routing: A more recent, highly streamlined technique involves the creation of "phantom wallets"—cryptocurrency addresses that possess no corresponding private key pair. Attackers encode C2 server internet protocols directly into the byte values of the phantom address. Infected endpoints are programmed to monitor zero-value transactions sent to these dead addresses, successfully extracting routing data without executing a standard data-carrying transaction.
These mechanisms afford attackers unprecedented campaign longevity. When law enforcement agencies or cybersecurity firms manage to block or seize an attacker’s traditional web infrastructure, the threat actor simply broadcasts a single new transaction or updates a smart contract variable. Every infected machine across the globe automatically pulls the new routing pointer during its next routine check-in, neutralizing the impact of the takedown.

Case Studies: DPRK, Iran, and Russian-Language Syndicates
Recent intelligence breakdowns highlight how distinct geopolitical and criminal factions have operationalized BDD technologies to advance their respective agendas.
In the case of North Korea, groups tracked by intelligence partners as UNC5342 have heavily relied on EtherHiding frameworks to target cryptocurrency developers and financial sector employees through elaborate social engineering and fake job interview ruses. More recently, investigations uncovered a sophisticated cross-chain redundancy model deployed by DPRK operators. This framework utilizes TRON and Aptos blockchains to store encoded pointers that resolve to a central transaction on the Binance Smart Chain. If a query on the TRON network fails, the malware seamlessly cascades to Aptos, ensuring that the infected device ultimately reaches the BSC payload regardless of network-level disruptions.

Simultaneously, threat actors assessed with high confidence to be linked to Iran’s Ministry of Intelligence have leveraged the Bitcoin blockchain. Rather than deploying complex smart contracts, Iranian operators utilize transaction-based storage by broadcasting small financial transactions to well-known, historically significant Bitcoin addresses—such as those associated with the network’s pseudonymous creator, Satoshi Nakamoto. The financial transfers themselves are economically irrelevant; the value lies entirely in the accompanying metadata, which infected devices decode to find current operational infrastructure.
On the commercial cybercrime front, Russian-language underground forums have begun treating BDD as a commodity through Malware-as-a-Service (MaaS) frameworks. Toolkits such as the ErrTraffic framework incorporate smart contract resolvers deployed on networks like Polygon and Binance Smart Chain. Affiliates rent these operational panels via subscription models, utilizing centralized deployer wallets to spin up fleets of storage contracts designed to manage everything from click-fix campaigns and fraudulent stablecoin tokens to sophisticated cryptocurrency-draining malware.

Implications for Global Cybersecurity and Defense Strategies
The proliferation of blockchain dead drops presents a profound operational challenge for enterprise security teams, financial institutions, and regulatory bodies. Because public blockchains rely on universally accessible peer-to-peer networks and public RPC endpoints, traditional network defense strategies—such as blocking outbound traffic to known blockchain providers—are entirely unviable. Enforcing a blanket ban on Ethereum or Bitcoin RPC traffic would inadvertently cripple legitimate financial technologies, decentralized applications, and enterprise web3 integrations.
Consequently, cybersecurity experts emphasize that defense strategies must shift away from network-level blocking and toward advanced attribution, behavioral analysis, and on-chain intelligence. By utilizing specialized blockchain analytics platforms, defenders can trace the lifecycle of deployer wallets, map out smart contract code reuse across disparate campaigns, and correlate on-chain funding sources with known threat actor profiles. Furthermore, monitoring corporate endpoint telemetry for anomalous or unauthorized JSON-RPC calls directed at public blockchain nodes can serve as a critical early-warning indicator that an internal machine has been compromised and is attempting to resolve an on-chain dead drop.

As open-source artificial intelligence tools continue to lower the barrier for writing complex smart contracts and custom malware strains, the volume of BDD activity is projected to climb. Mitigating this persistent threat will require unprecedented levels of operational collaboration between traditional cybersecurity investigators, blockchain analytics firms, and international law enforcement agencies to map, disrupt, and neutralize web3-enabled cyber campaigns at their source.
