The Ethereum Foundation’s ongoing Trillion Dollar Security initiative has identified the dual perils of blind signing and transaction uncertainty as significant barriers to mass adoption, prompting an exploration of native transaction assertions as a foundational security layer. This proposal, intended to operate alongside the previously announced Clear Signing initiative, seeks to enforce specific, user-defined outcomes for blockchain transactions, ensuring that a valid signature translates into the intended financial result. By addressing the fundamental disconnect between authorized intent and execution outcome, the foundation aims to mitigate systemic risks that have historically led to substantial capital losses.
The Problem: Intent vs. Execution in the EVM
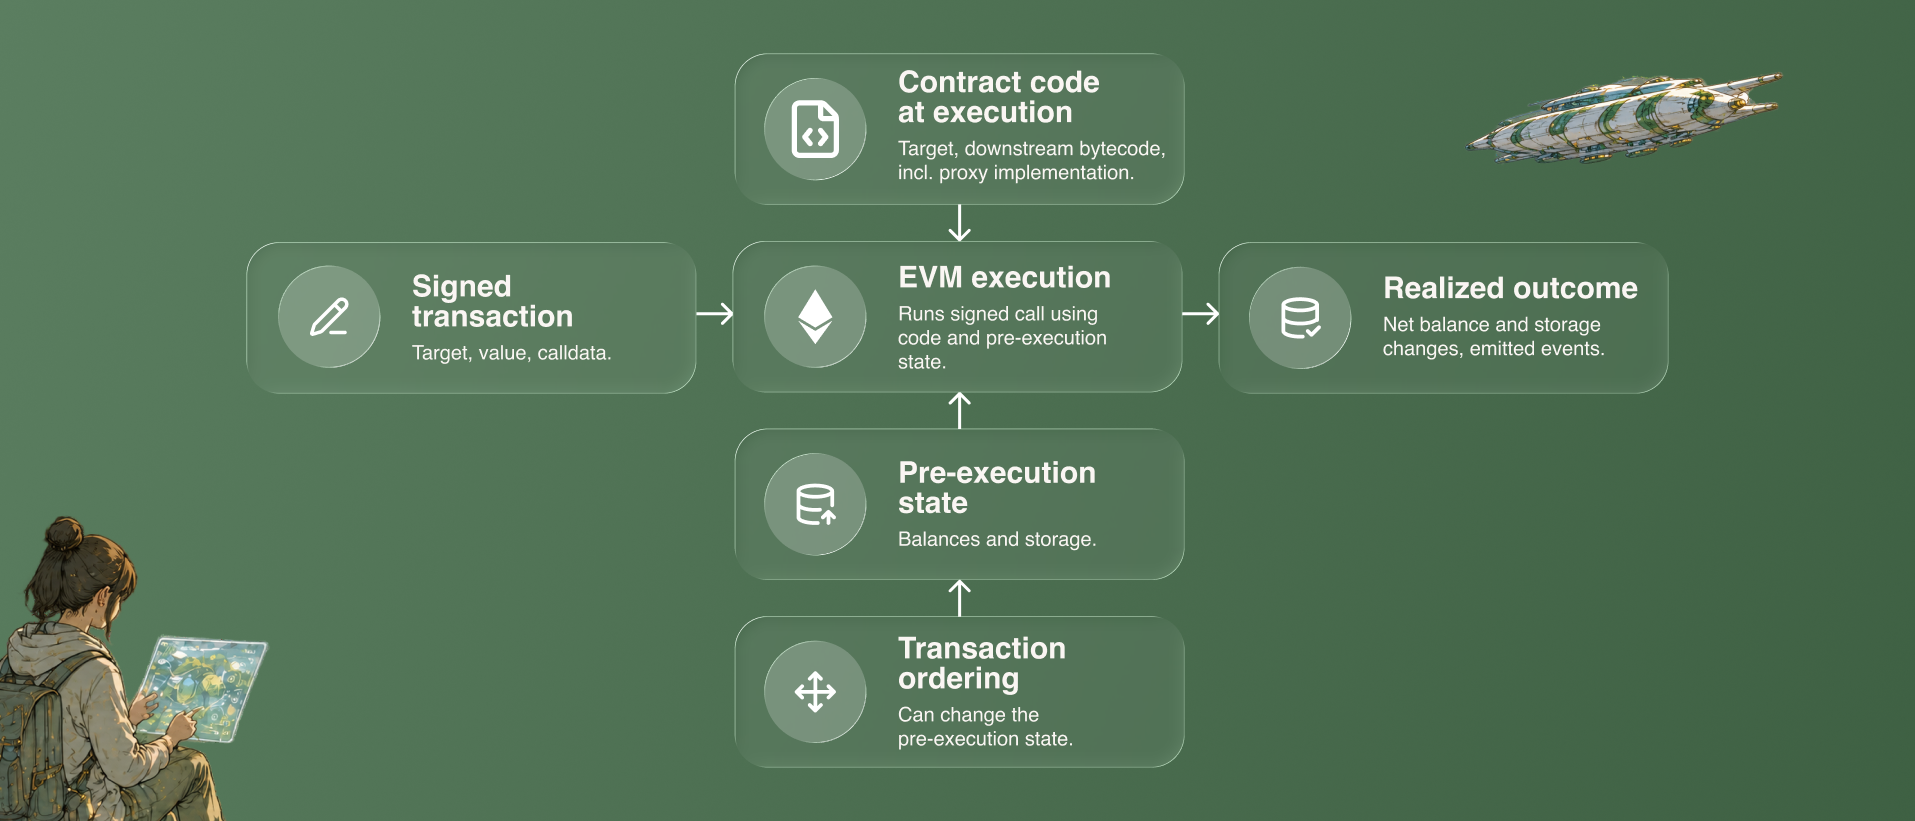
At the core of the issue is the inherent design of the Ethereum Virtual Machine (EVM). When a user signs a transaction, they are essentially providing a cryptographic mandate for the network to execute a specific set of instructions. However, the EVM operates in a reactive manner; it executes the code and interacts with the state exactly as it exists at the moment of inclusion, without verifying whether the resulting state matches the user’s original intent.
This architecture has proven catastrophic in several high-profile security incidents. In the Bybit-related Safe wallet incident, attackers leveraged a compromised frontend to manipulate signing requests, resulting in users inadvertently authorizing the replacement of critical implementation contracts. Similarly, the BadgerDAO attack demonstrated how malicious actors could trick users into granting excessive token permissions. In both instances, the signature was technically valid, yet the transaction’s outcome was diametrically opposed to the user’s perception of the action.
These failures highlight a critical limitation in current blockchain security: the lack of a "result-guarantee" mechanism. The user signs for a process, but the outcome is dictated by external state variables, such as contract implementation addresses or current liquidity pool prices, which can change in the milliseconds between signing and final block inclusion.
A Chronology of Vulnerability and Defense
The history of Ethereum security is marked by a constant race between innovation and exploitation. Early defense mechanisms focused on "what" was being signed—efforts like Clear Signing strive to provide human-readable transaction summaries to prevent users from unknowingly approving malicious actions. While vital, these tools are often bypassed by sophisticated social engineering or interface compromises, such as the Radiant Capital exploit, where the malicious payload was injected at the exact moment of signing.
Beyond malicious intervention, there is the issue of "outcome mismatch," where the transaction is legitimate but the economic result is disastrous. In the notable Aave and CoW Swap incident, a user attempted to swap roughly $50.4 million in aEthUSDT for aEthAAVE. Due to thin liquidity and a lack of granular, enforceable constraints on the transaction’s outcome, the user received only a fraction of the expected value—approximately $36,000. Despite a 99.9% price impact warning, the absence of an on-chain, mandatory assertion regarding the minimum acceptable output meant the transaction proceeded, resulting in a staggering loss.
The Mechanics of Native Transaction Assertions
The proposed solution, formalized in EIP-7906, introduces a "POST_TX" frame that acts as a final gatekeeper. By utilizing a read-only logic layer, this framework allows the blockchain to compare the initial state of an account with its final state after the execution of the main transaction. If the resulting state—be it a balance, a storage slot value, or a specific contract deployment—does not align with the pre-signed, user-defined assertion, the EVM triggers a total revert of the transaction.
This is a departure from current "guard" systems, such as the Safe checkAfterExecution hook, which are often limited by the functions the target contract chooses to expose. If a proxy contract does not explicitly provide a getter function for its implementation address, traditional guards remain blind to unauthorized changes. Native assertions, by contrast, function at the protocol level, allowing the EVM to inspect the full scope of net state changes, including ETH balance shifts, token movements, and internal storage mutations.
Design Philosophies: EIP-7906 and Beyond
EIP-7906 represents a sophisticated evolution of the "frame transaction" concept, which is currently being built upon the foundations laid by EIP-8141. By introducing three specific opcodes—TXTRACE, TXDIFF, and EVENTDATACOPY—the protocol empowers developers to write precise rules for transaction success.
- TXTRACE: Enables the enumeration of all net state changes and emitted events, providing a comprehensive audit trail of the transaction’s impact.
- TXDIFF: Allows for the retrieval of starting and final values for specific storage slots, enabling users to enforce that certain variables (like an implementation contract address) remain immutable.
- EVENTDATACOPY: Facilitates the extraction of event data into memory, ensuring that off-chain monitoring systems can verify the internal logs of a transaction execution.
Importantly, these opcodes are designed to execute within a static call frame, ensuring that the assertion itself cannot modify the state, but rather only observe and validate the outcome of the preceding steps. This design prevents a circular dependency where the assertion could introduce its own risks.
Broader Implications and Strategic Importance
The implementation of native transaction assertions would carry significant implications for the future of decentralized finance (DeFi). For institutional and professional users, the ability to define rigorous, on-chain safety policies—such as capping total slippage, blocking unauthorized new approvals, or ensuring that a specific smart contract remains at a predetermined address—would provide a level of security previously unavailable in a permissionless environment.
Moreover, this technology would redefine the relationship between users and "solvers" or automated agents. In modern solver-based architectures, the user often trusts the solver to find the best route. With native assertions, the user can maintain sovereignty, defining the acceptable bounds of the trade while delegating the execution logic to the agent. If the solver fails to provide the promised outcome, the transaction automatically reverts, protecting the user’s capital without requiring constant manual oversight.
The Road Ahead: Challenges and Collaboration
Despite the technical promise, the Ethereum Foundation acknowledges significant challenges. The primary obstacle is adoption: EIP-7906 does not mandate assertions for all transactions. If a wallet or a user fails to include a required assertion, the transaction remains vulnerable to the same risks that exist today.
Furthermore, the design must carefully balance developer flexibility with protocol performance. The computational overhead of tracking state changes and verifying them at the end of a transaction must be optimized to ensure that transaction throughput does not suffer.
The Foundation is currently soliciting feedback from major wallet developers, security auditors, and protocol architects to refine these specifications. As the research continues, the emphasis remains on creating a standardized, user-centric security model that can scale across the entire Ethereum ecosystem. Interested parties are encouraged to engage with the Ethereum Magicians community or contact the Trillion Dollar Security initiative directly.
Ultimately, the shift toward native transaction assertions represents a maturation of the Ethereum network. By moving from a "hope for the best" execution model to one based on "verifiable intent," the Ethereum Foundation is positioning the network to handle the complexities of institutional-grade financial activity while simultaneously protecting the individual user from the persistent threats of the digital asset landscape. Whether through EIP-7906 or future iterations of this concept, the integration of outcome-based validation appears to be the next logical step in the evolution of secure, decentralized computation.